
When it comes to causing a meltdown, Grok never disappoints.
Just recently, security firm Claroc discovered that over 35,000 apps built with Grok could be accessed without logging in—some of which directly exposed corporate secrets and personal privacy.
What stands out the most is that Elon Musk’s own companies, SpaceXSI (the company formed after the merger of SpaceX and xAI) and X, are among the victims.
Employee onboarding plans, sales client profiles, advertising proposals… even their own dirty laundry was aired out in public.
Moreover, the unmerged Tesla didn’t escape unscathed either. A service center scorecard placed the names, efficiency metrics, and bonus details of 22 technicians right onto a public webpage.
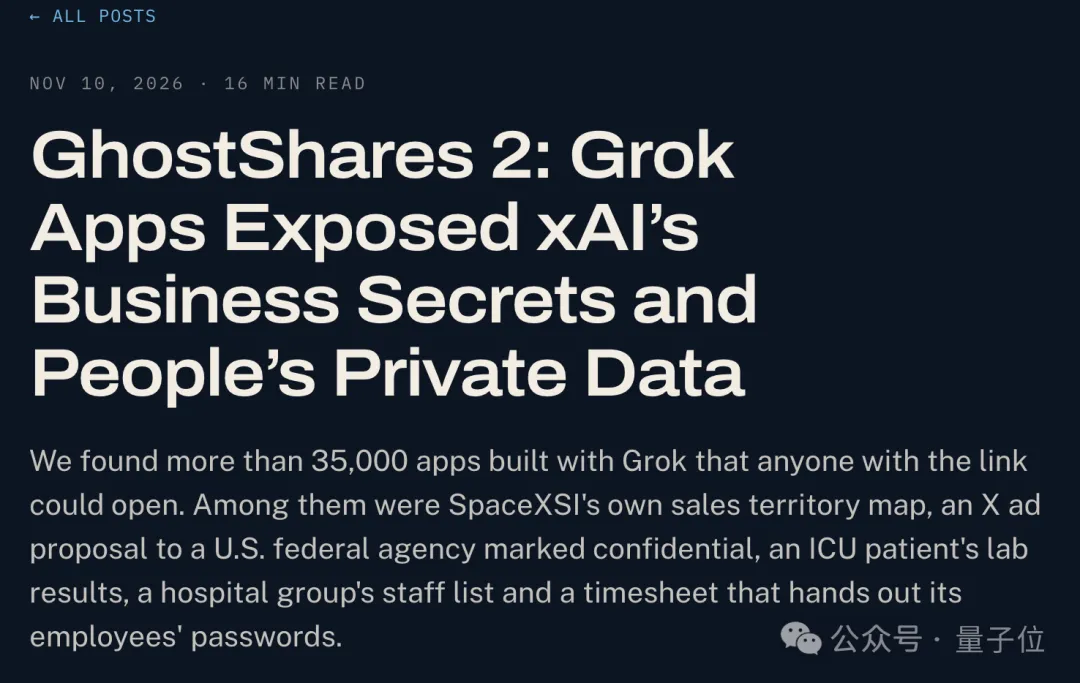
Even more outrageous is that it wasn’t just their own employees getting burned by dogfooding their own product; the leaked content also involved sensitive information of everyday people.
This included lab results, imaging scans, and ventilator usage records of ICU patients, as well as plaintext account passwords of corporate employees.
Holy moly, does using Grok really come with a free one-click doxxing service?
What Exactly Was Leaked?
Specifically, at the beginning of the investigation, Claroc tested 43,551 Grok Build app URLs (37,571 of which were still online) and found that 94.7% of the active apps could be opened without logging in.
While most of these apps are just AI slop created by everyday users like you and me—things like mini-games or calculators…
By sifting through the noise using model screening and manual sampling, Claroc estimated that roughly 650 to 800 apps contained private data.
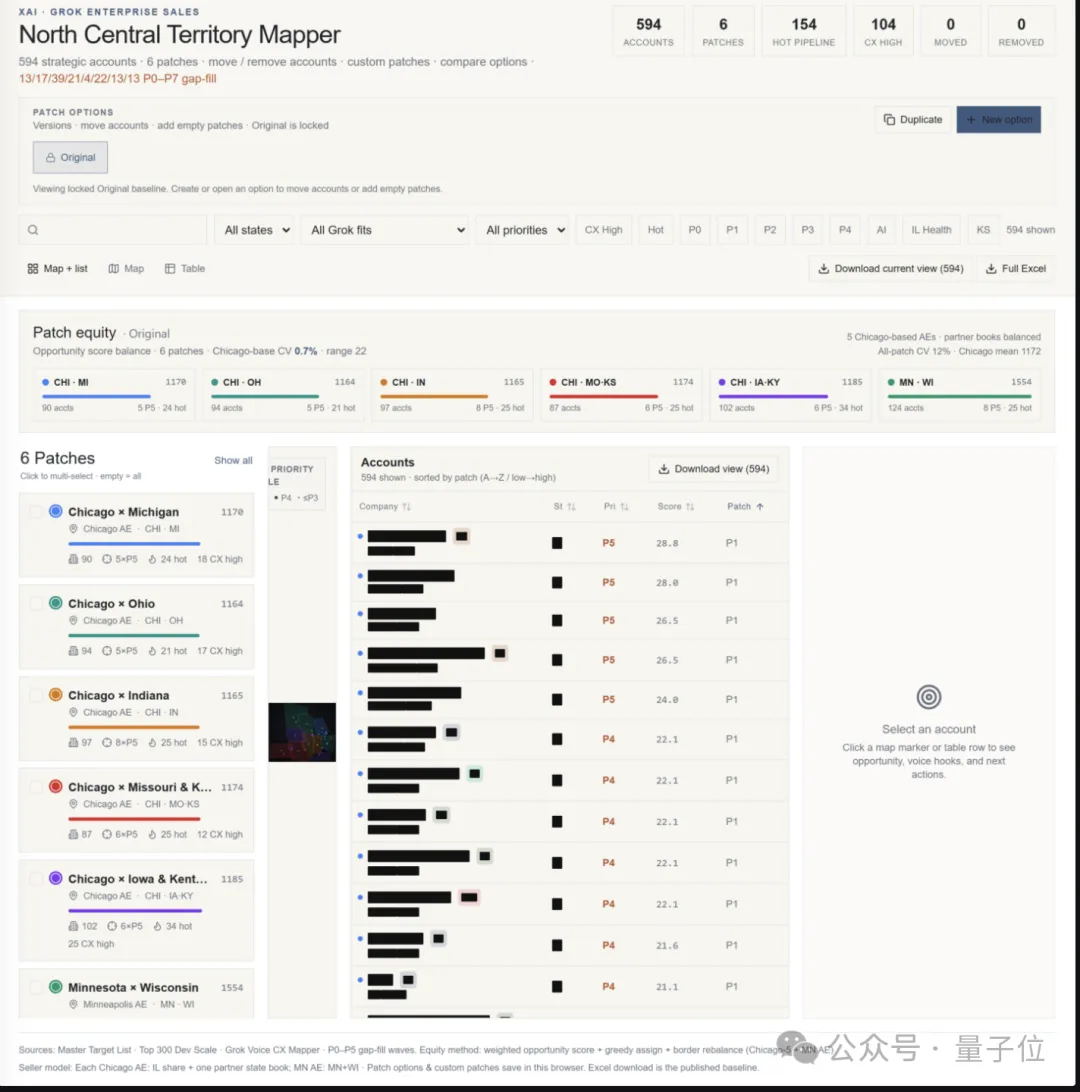
The affected organizations include SpaceXSI, X, and 30 other companies, 6 of which are Fortune 500 enterprises.
How sensitive is this data? A few examples will give you an idea:
-
An ICU patient briefing containing patient lab results, imaging scans, and ventilator usage status.
-
A contractor’s time-tracking app that hardcoded plaintext passwords for 18 accounts directly into a script, which anyone visiting the page could download.
-
An internal sales tool for SpaceXSI containing strategic client accounts, sales opportunities, and internal team information.
-
A Tesla service center scorecard containing employee names, efficiency metrics, and bonus details.
…
Looking at this, while you have to wonder who in their right mind puts their passwords and medical records into a Vibe Coding project, the fact that Grok just broadcast them to the entire world is truly wild.
So, how did this data—which was supposed to circulate strictly within company walls—end up on public webpages?
How Did a Random Link Become a Doxxing Portal?
Simply put, when you use Grok for Vibe Coding, it assigns a unique URL to each published app, formatted like 随机名称.grok.me.
These random names are made up of several words, originally designed to make them difficult for others to guess. The problem is, an unguessable URL does not equal secure access control.
Claroc discovered that these app URLs could be found in bulk through Passive DNS databases.
In simple terms, whenever someone visits a website, their computer has to query DNS to find the server address corresponding to the domain name. Some DNS resolution services collect these query records and put them into searchable databases.
Thus, a discovery path was formed:
Someone visits the app → The DNS query leaves a record → The domain enters a Passive DNS database → External parties harvest the app URLs in bulk.
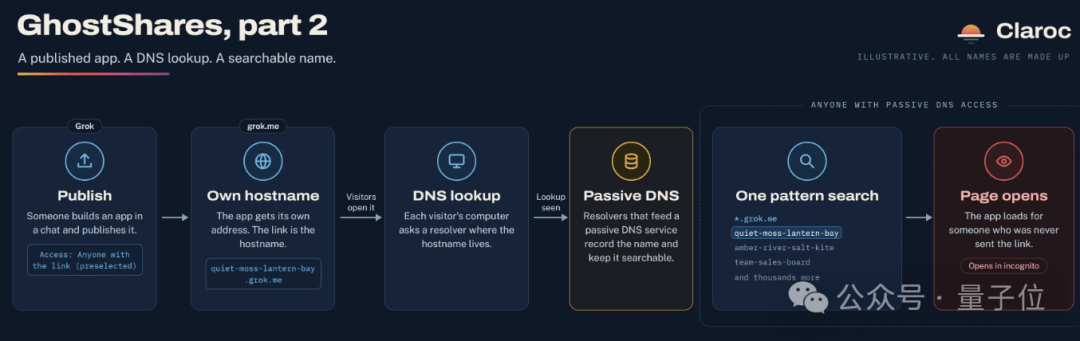
If an app’s access permission is set to “Anyone with the link,” then anyone who finds the URL can open it directly.
In other words, Grok used random URLs to make apps harder to find, but failed to actually solve the access control problem.
To be fair, Claroc also ran a control test using ChatGPT apps: while their app URLs can also be indexed by Passive DNS, the sharing panel defaults to “Only me.” Even if someone finds the URL, they cannot access it.
Score one for ChatGPT!
Furthermore, to verify whether the code generated by Grok is reliable and how it handles team permissions, Claroc subsequently built a customer management app for a four-person sales team using fictional data.
Although Grok did automatically add Google and X login functionality, researchers inspected the code and found a rookie mistake:
The app adds the person logging in to the team first, and only then checks if they are a team member. That’s like inviting someone into a group chat first, and then checking if they belong to the group.
Well, of course they’re going to be in the group then…
Next, the researchers logged in using a Google account that had never been invited. Not only did they see all the customer profiles, but they also successfully modified one record and deleted another.
In short, as long as you want in, Grok’s doors are always wide open for you.
Official Response and Follow-up
After the incident came to light, SpaceXSI told the media that apps are private until the creator actively shares them, and that publishing requires going through multiple steps.
The company also claimed that its employee accounts default to “Only you,” and making an app public requires actively changing the permissions.
However, Claroc stated that in the paid account they used for testing, the publish panel came pre-selected with “Anyone with the link.”
Here lies the crux of the matter:
Being private before publishing, and who gets access by default when publishing, are two completely different things.
If a user clicks all the way through to “Publish” and the pre-selected access scope remains “Anyone with the link,” adding a few more confirmation prompts isn’t going to magically populate a list of authorized team members.
Researchers also verified Grok’s existing access control features.
After switching the setting to “Only you,” strangers attempting to access the page and data APIs were denied; unpublishing also took the app offline within seconds.
So, Grok does have working protective measures. The question is whether these measures were actually put to use when users published their internal tools.
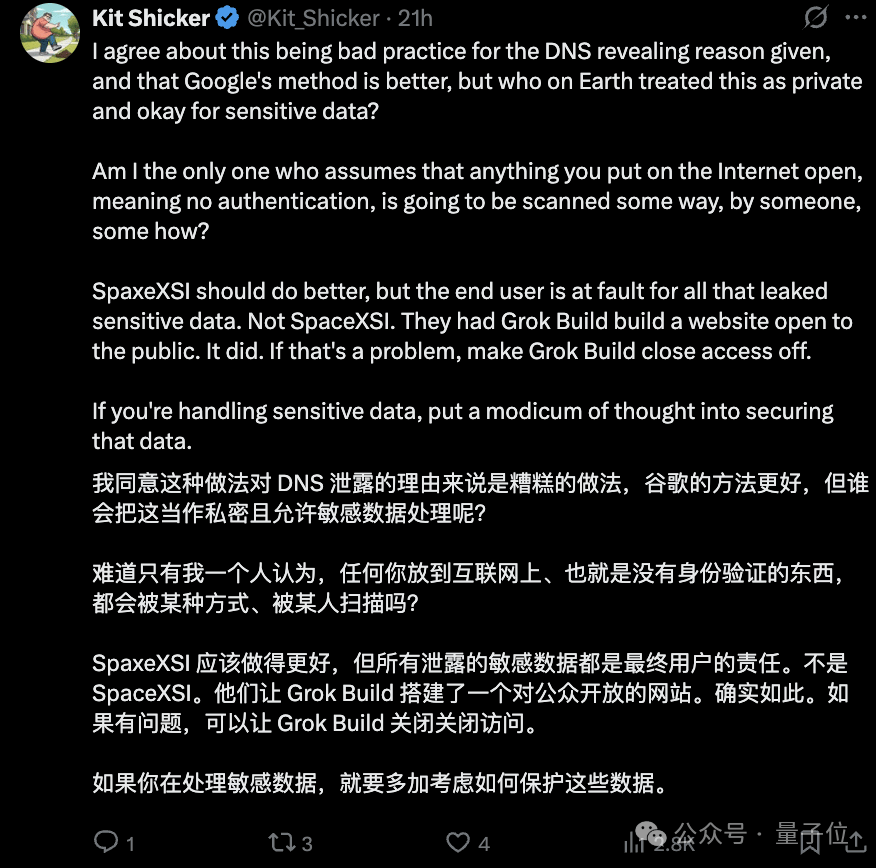
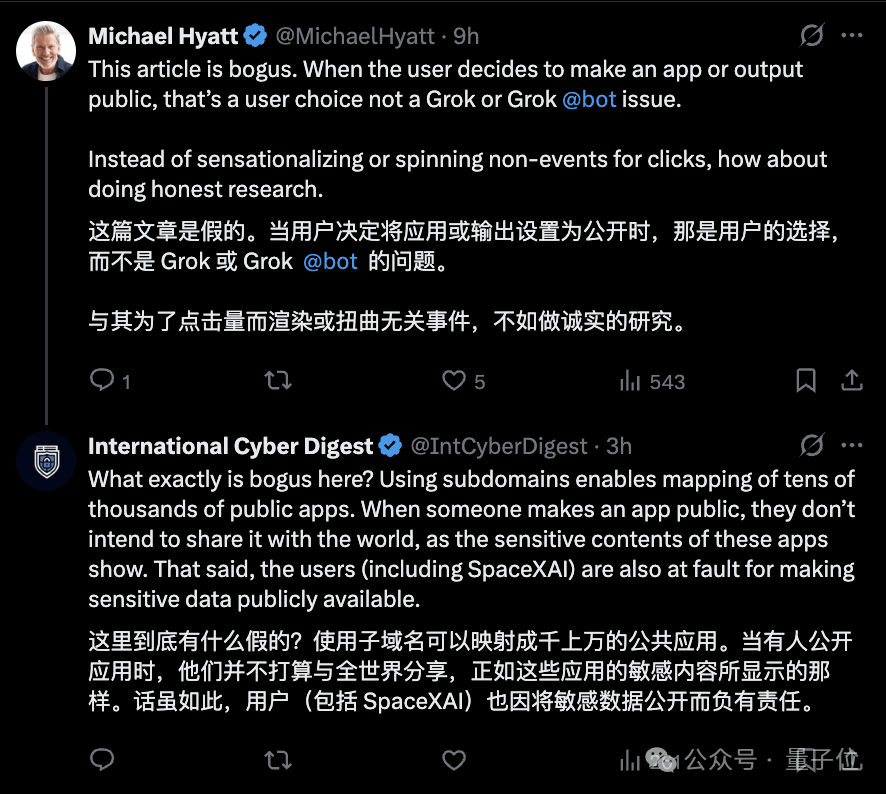
Currently, a heated debate has broken out on X (formerly Twitter) over this issue, with some blaming users for opening up permissions themselves, and others blaming Grok’s flawed permission settings.
As for the aftermath, SpaceXSI only began removing the affected links within a few hours after Ars Technica sent an email requesting comment.
By the time the report was published, all 24 apps created by SpaceXSI and X employees had been taken offline.
However, a massive number of apps created by other users remain accessible, and Claroc has begun reaching out to the affected organizations on its own.
As for whether the platform will proactively notify other affected customers, Ars Technica has yet to receive a clear answer.
References:
[1] https://arstechnica.com/security/2026/11/grok-build-coding-agent-leaks-oodles-of-confidential-info-some-belonging-to-spacexsi/
[2] https://blog.claroc.io/ghostshares-grok-build-apps/