
All digging, no patching.
Lately, the reality of AI bug-hunting has felt remarkably fractured.
On one hand, AI is conducting sweeping audits of legacy code, first uncovering a major underlying security vulnerability in PHP, and immediately following that up by unearthing 948 Linux kernel vulnerabilities…
On the other hand, the open-source community is on the verge of a breakdown: You found all these vulnerabilities—now how about fixing them?!
Yesterday, the cybersecurity firm VulnCheck released a report card on Anthropic’s Project Glasswing.
The report reveals that seven months after the launch of Project Glasswing, Claude has uncovered a cumulative total of 37,966 candidate vulnerabilities.
Yet to date, public records show that only 217 of them have been remediated.
VulnCheck couldn’t help but question: Has the much-hyped “Mythos Era” of cybersecurity really arrived?
Out of 38,000 Vulnerabilities, How Many Have Actually Been Fixed?
First, let’s recap “Project Glasswing,” which Anthropic launched with great fanfare this past April.
The initiative aims to use Claude to discover security vulnerabilities at scale across critical software and open-source projects, partnering with tech companies and open-source maintainers to drive remediation and eliminate security risks before they can be maliciously exploited.
The name carries a double meaning: On one hand, security vulnerabilities—much like the glasswing butterfly—can hide in plain sight for decades without being noticed. On the other hand, transparency itself is a form of protection; Anthropic hopes to better safeguard software systems through more transparent security research and vulnerability disclosure mechanisms.
△ Glasswing butterfly, scientific name Greta oto | Source: Wikipedia
At launch, Anthropic pledged $100 million in model usage credits and $4 million in open-source security donations, while announcing that its flagship cybersecurity model, Claude Mythos Preview, had already discovered thousands of high- and critical-severity vulnerabilities. The initiative quickly drew widespread support, with tech giants like Apple, Google, Microsoft, AWS, and NVIDIA joining in.
But has it really lived up to the hype?
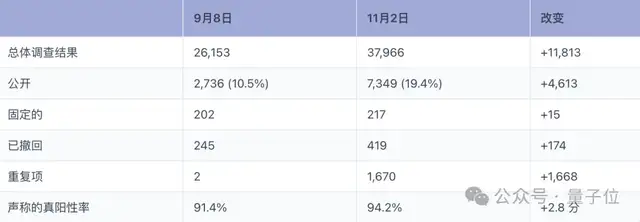
According to continuous tracking data from VulnCheck, as of early November, Anthropic’s candidate findings reached 37,966, yet only 217 were marked as remediated in the vulnerability disclosure ledger.
Meanwhile, invalidated data continues to pile up, including 419 withdrawn entries and a staggering 1,654 duplicates.
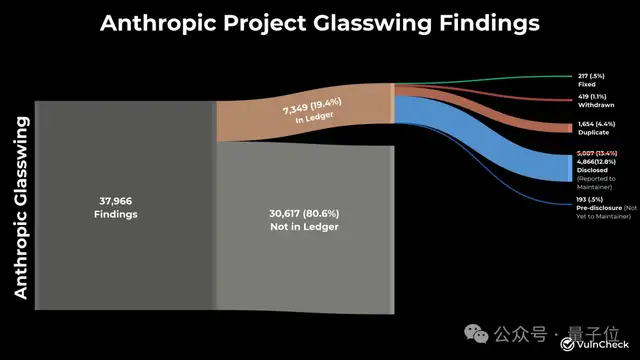
△ Source: VulnCheck
And this gap is widening at an accelerating pace.
In just the last two months alone, candidate vulnerabilities surged by nearly 12,000, while remediated records saw a meager increase of just 15.
Furthermore, the 442 CVEs (Common Vulnerabilities and Exposures) attributed to Anthropic and tracked by VulnCheck account for a mere 0.5% of the global public CVE total in 2026.
 △ Source: VulnCheck
According to official data disclosed by Anthropic, as of November 2, out of the 37,966 candidate findings, 6,376 have been reviewed by external security experts, confirming 6,009 as valid findings. So far, 5,087 findings have been reported to software maintainers, and 629 have received upstream patches.
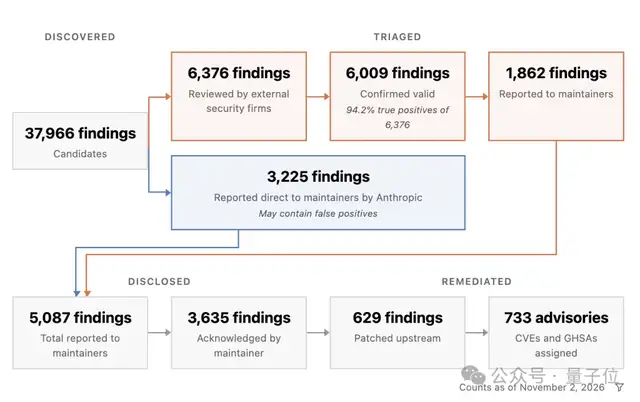
Although differing counting methodologies have led to slight discrepancies in the number of fixes, both sides have noticed the exact same problem:
Human reviewers simply cannot keep up with the sheer intensity of AI vulnerability discovery.
Anthropic realized this early on. The company candidly admitted that severe bottlenecks in human verification capacity have significantly bottlenecked the efficiency of vulnerability triage and disclosure.
Consequently, on October 8, Anthropic launched a service called OSS Scanner.
Open-source project maintainers can proactively sign up to have Claude scan their code for free. This way, vulnerability reports generated by the model are sent directly to the maintainers without waiting for Anthropic to organize a manual review.
Open-Source Maintainers Are Overwhelmed
AI is forcing us to immediately pay off 40 years of accumulated technical debt.
Behind this massive data gap, the ones suffering the most are open-source maintainers. VulnCheck used the network data transfer tool curl as an example to illustrate this reality.
In early November, curl maintainer Daniel Stenberg received yet another “care package” from Anthropic—45 vulnerability reports.
Even before this, Daniel had written on his blog that core maintainers were being suffocated by the relentless flood of incoming reports:
We aim to not drown.
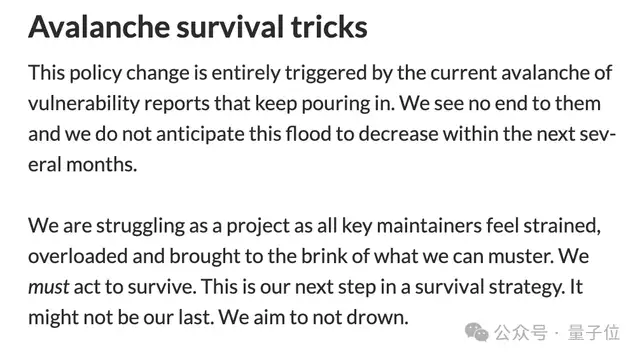
To cope with such an overwhelming volume of reports, Daniel announced changes to curl’s security vulnerability handling policy: moving discussions of low- and medium-severity vulnerabilities to public GitHub threads so more community developers can help with triage.
Currently, out of the 34 reports made public by curl, 19 have been determined not to be security vulnerabilities at all, and 6 have been confirmed as low-severity vulnerabilities.
VulnCheck subtly mocked this in their report, asking: Weren’t these supposed to be all critical threats? Why does it look like Project Glasswing isn’t doing much beyond piling extra review work onto people’s plates?
In fairness, however, Anthropic did help curl uncover one critical vulnerability.
This past September, using Claude, Anthropic discovered a Use-After-Free memory bug in curl. Under specific conditions, a malicious server could potentially exploit it to achieve remote code execution.
Daniel noted that this was one of the most severe vulnerabilities curl had seen in years.
That being said, VulnCheck’s report also reads a lot like a self-promo—because the exact pain points of Project Glasswing that it criticizes happen to align perfectly with the vulnerability intelligence and prioritization services that VulnCheck itself sells…
One More Thing
At this point, some might wonder: If Claude is so capable, why doesn’t it just fix the bugs right as it finds them?
In fact, Anthropic is already having AI generate candidate patches.
It’s just that developers have long suffered from “AI-generated bug fixes”… As one netizen put it: “Getting an LLM to generate a fix isn’t hard; the hard part is getting an open-source project to actually accept it.”
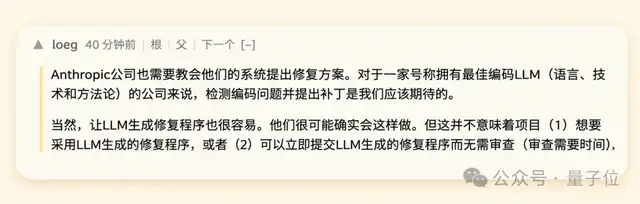
The workload required to review an AI-generated patch is sometimes almost equivalent to writing it from scratch yourself.
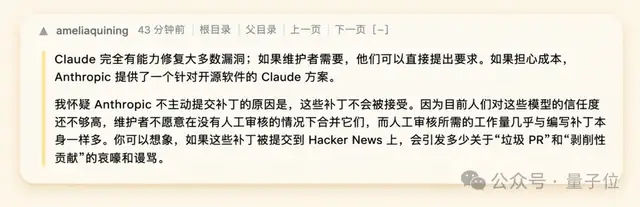
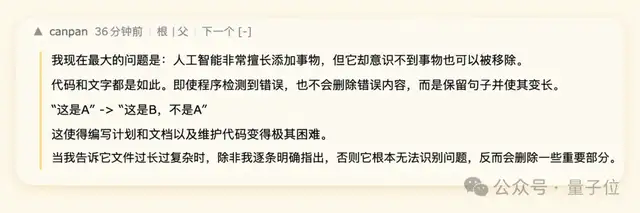
The situation often feels like “lighting a candle only to illuminate more darkness”: the AI finds an issue and starts fixing it, but in doing so, it introduces even more complex logic into the codebase; ultimately, it fixes one bug while creating ten new ones.
“AI is great at adding things, but it doesn’t realize that some things can actually be removed…”
So at least for now, the holes dug up by these frontier models still have to be filled in by humans.
Reference Link:
https://www.vulncheck.com/blog/anthropic-glasswing-november-update